PeterMendis
open-menu closeme
Home
About
English
github twitter linkedin rss
  • Encrypting Data at Rest for Kafka Workloads with Kroxylicious

    calendar Nov 8, 2026 · 7 min read · Kafka Kroxylicious Encryption
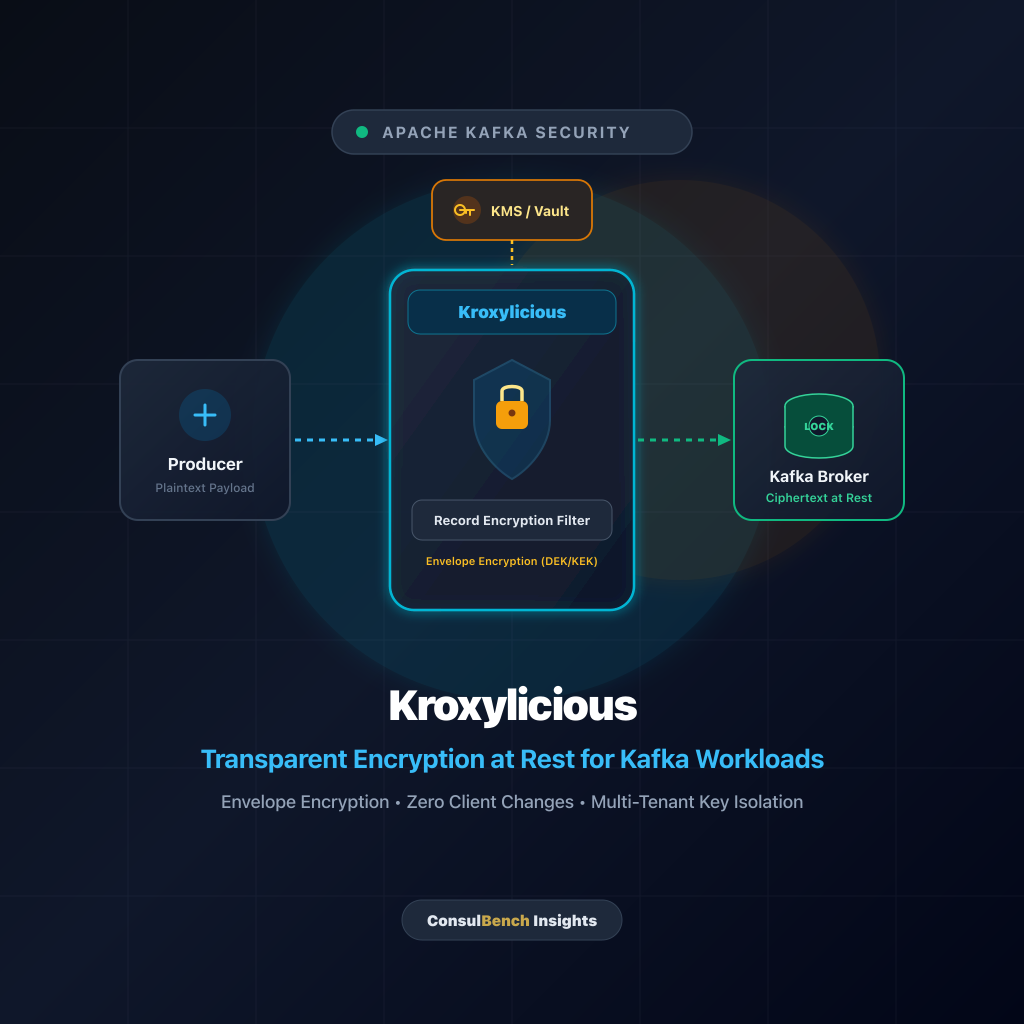
    Encrypting Data at Rest for Kafka Workloads with Kroxylicious

    In enterprise event streaming, securing data at rest is a non-negotiable compliance requirement. Whether adhering to PCI-DSS, HIPAA, or strict financial industry mandates, organizations must guarantee that sensitive data stored within Apache Kafka cannot be accessed by unauthorized parties. However, standard …


    Read More
  • SPIFFE / SPIRE for managing AI workload Identity

    calendar May 31, 2025 · 8 min read · AI Security Workload Identity SPIFFE Kubernetes
    SPIFFE / SPIRE for managing AI workload Identity

    SPIFFE (Secure Production Identity Framework for Everyone) and SPIRE (SPIFFE Runtime Environment) offer a powerful solution for managing identities in dynamic, distributed systems. This makes them highly relevant for securing Generative AI and Agentic AI workloads, which inherently involve complex interactions between …


    Read More
  • Authenticating applications using OpenID Connect on K8s using Sidecar - Part 2

    calendar Jul 6, 2020 · 5 min read · k8s open-id oauth2 keyclock kubernetes
    Authenticating applications using OpenID Connect on K8s using Sidecar - Part 2

    Welcome to Part-2 of "Authenticating web applications using OpenID Connect without having to change to app code" I am going to follow this article from openshift to setup and configure OpenID-Client Client Here is the summary of things that you need to perform and you could follow the above article. You have to create …


    Read More
  • Authenticating applications using OpenID Connect on K8s using Sidecar - Part 1

    calendar Jul 4, 2020 · 2 min read · k8s open-id oauth2 keyclock kubernetes
    Authenticating applications using OpenID Connect on K8s using Sidecar - Part 1

    I am going to author multiple articles under application authentication using popular industry standard method known as OAuth2.0. I will be using OpenID connect in this example. In Part-1, I will be covering deploying opensource keycloak (Identity and access management software) on kubernetes and adding users to access …


    Read More

Peter Mendis

Technologist, opensource advocate, learner, platform engineering, solutions architect, cloud native evanglist.
Read More

Featured Posts

  • Encrypting Data at Rest for Kafka Workloads with Kroxylicious
  • SPIFFE / SPIRE for managing AI workload Identity
  • What are Kamelets?

Recent Posts

  • Nomad setup for multi node development server
  • Kubernetes the Hardway using LXD
  • Solving complex state updates using Kafka CQRS
  • Authenticating applications using OpenID Connect on K8s using Sidecar - Part 2
  • Authenticating applications using OpenID Connect on K8s using Sidecar - Part 1
  • Running Elasticsearch, FluentD, Kibana (EFK) on OKE

Categories

SECURITY 4 TECHNOLOGY 4 CONTAINERS 2

Series

SECURITY AUTHENTICATION USING SIDECAR 2

Tags

K8S 4 KUBERNETES 4 CONTAINERS 2 JAVA 2 KAFKA 2 KEYCLOCK 2 OAUTH2 2 OPEN-ID 2 AI SECURITY 1 APACHE CAMEL 1 CEP 1 CQRS 1 CRD 1 EFK 1
All Tags
AI SECURITY1 APACHE CAMEL1 CEP1 CONTAINERS2 CQRS1 CRD1 EFK1 ELASTICSEARCH1 ENCRYPTION1 EVENT STREAMING1 INDEX1 JAVA2 K8S4 KAFKA2 KEYCLOCK2 KROXYLICIOUS1 KUBERNETES4 LOGS1 NOMAD1 OAUTH22 OKE1 OPEN-ID2 ORCHESTRATION TOOL1 SPIFFE1 WORKLOAD IDENTITY1
[A~Z][0~9]
Copyright © 2025, Peter Mendis; all rights reserved.

Copyright  COPYRIGHT © 2025, PETER MENDIS; ALL RIGHTS RESERVED.. All Rights Reserved

to-top